MANAGED XDR · 24/7 CYBER DEFENSE CENTERS

One platform,
all-out protection

Detect and contain cyber threats in minutes, not days.
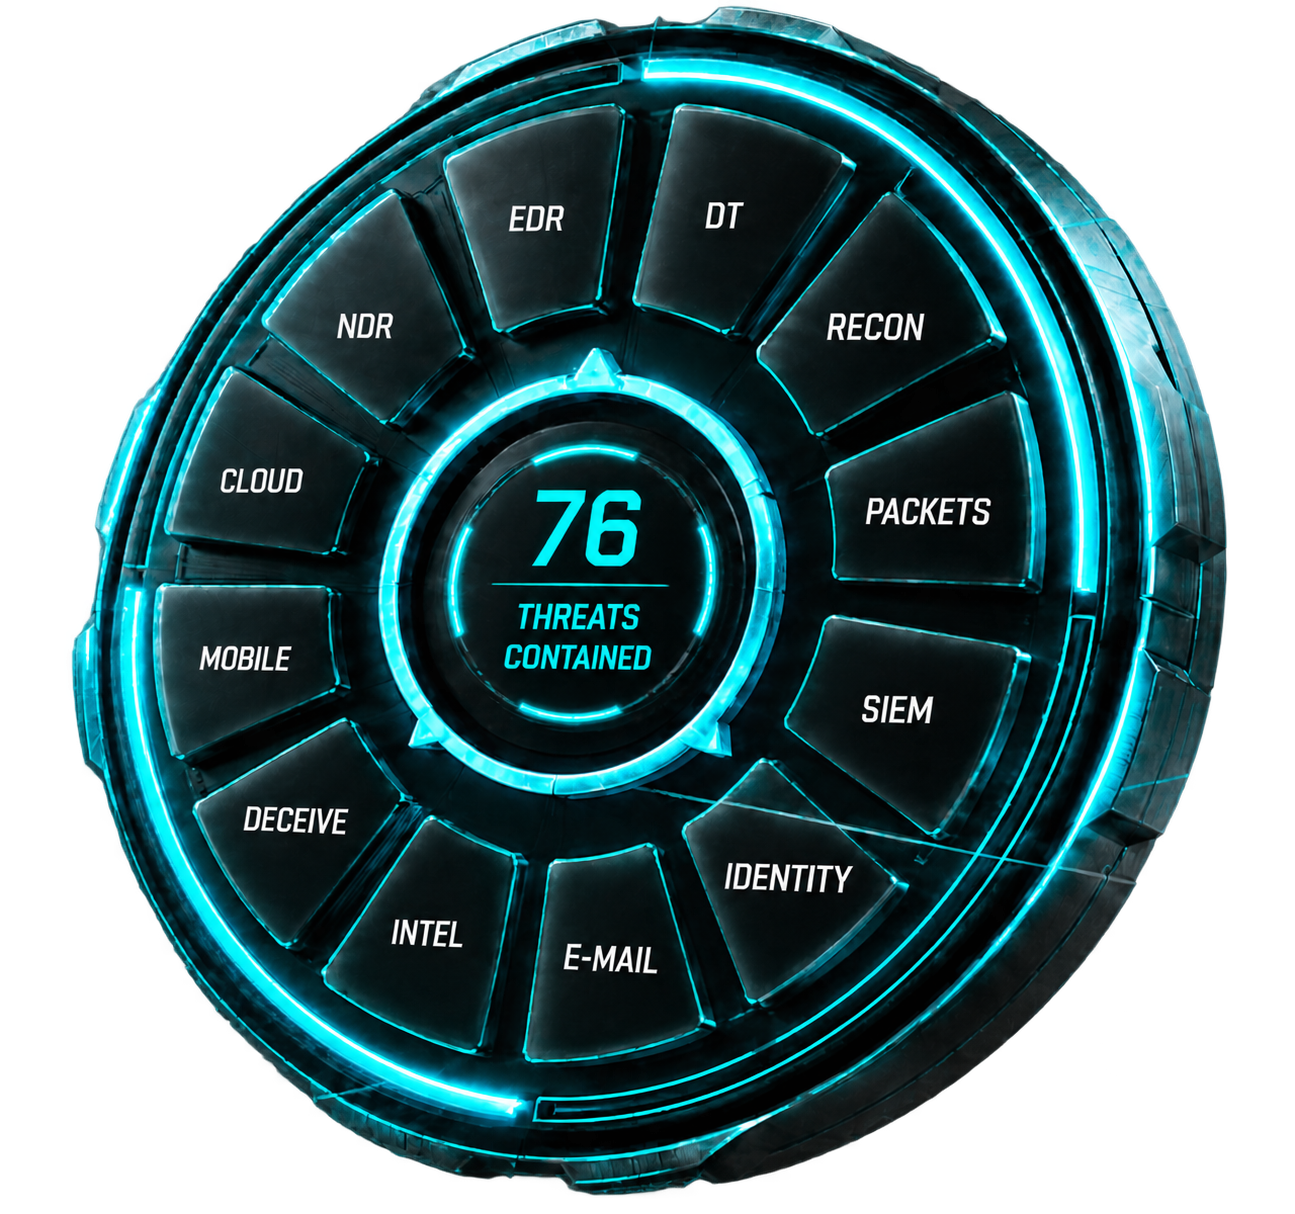
Active Defense platform wheel
< 30 minMean time to remediate ¹
98%Fewer alerts reaching your team ¹
85%+lower cost than building an in-house SOC
400+Customers across 85+ countries ¹

¹ Response times are LMNTRIX MDR service targets measured across confirmed incidents.

CONTINUOUS RESPONSE

How we protect small and large enterprises

We know that every day you have everything on the line, and that with so much at risk it can seem like adversaries have all the advantages. Together we can take the power back. Where other cybersecurity providers see a vendor and a customer, we see a united team of defenders who are stronger as one.

RECOGNIZED BY INDUSTRY ANALYSTS

TRUSTED BY CUSTOMERS AROUND THE WORLD

A sheep — the organisation that trusts its tools / A wolf — the hunter that finds the attacker

THE PROBLEM

Assume breach. Prove otherwise.

YOUR STACK TODAY

Your tools guard the door.
None see who's already in.

Firewalls, EDR, and SIEM create walls. Attackers walk around them, then disappear into alert noise.

  • Alerts say something happened.
  • Each tool sees one domain.
  • Relies on controls holding.

Intrusions go unnoticed for weeks.

XDR UNLIKE ANY OTHER

Deployed behind your controls.
Because we assume they’ve already failed.

  • NGAV, EDR, NDR, cloud and identity in one platform, with built-in deception.
  • Detects threats your existing tools miss.
  • Automated response across LMNTRIX XDR and third-party tools from one console.

HERE’S WHY

SIEM just doesn’t cut it anymore.

Let’s talk about the elephant in the room. Raise your hand if you’ve been let down by your SIEM. Wow. That’s a lot of hands.

LMNTRIX has reimagined cybersecurity, turning the tables in favor of the defenders once again. We have cut out the bloat of Stupidly Irrelevant Electronic Messaging (SIEM) alerts and log analysis, creating new methods for confounding even the most advanced attackers.

  • Endless false positives

    The boy had cried wolf too many times.

  • Endless alert fatigue

    Only one percent of all attacks are detected through logs.

  • Endless cost

    Cybersecurity doesn’t need to be expensive to be effective.

CONTINUOUS RESPONSE

Every Second Counts

Reverse the adversary advantage with laser-accurate detection and lightning-fast investigation and response

01 min

Detect < 1 Minute

05 min

Investigate < 5 Minutes

30 min

Remediate < 30 Minutes

  1. Deploy

    Seamless deployment and operational in hours, not days

  2. Detect

    Instant threat detection across all endpoints while we onboard the rest of our tech stack.

  3. Investigate

    We investigate and take action on your behalf to stop threats from disrupting your business.

  4. Remediate

    Our team quickly learns the who, what, when, and how of an attack, and responds to threats in minutes using the autonomous containment and remediation features built into our XDR.

  5. Report

    We identify the root cause of threats and provide detailed reports with the threat breakdown to prevent future incidents.

Not a managed SIEM. A Cyber Defense Center that acts for you, 24/7.

THE GAME CHANGER

You’re ready for
advanced protection

And that means XDR
See LMNTRIX in action
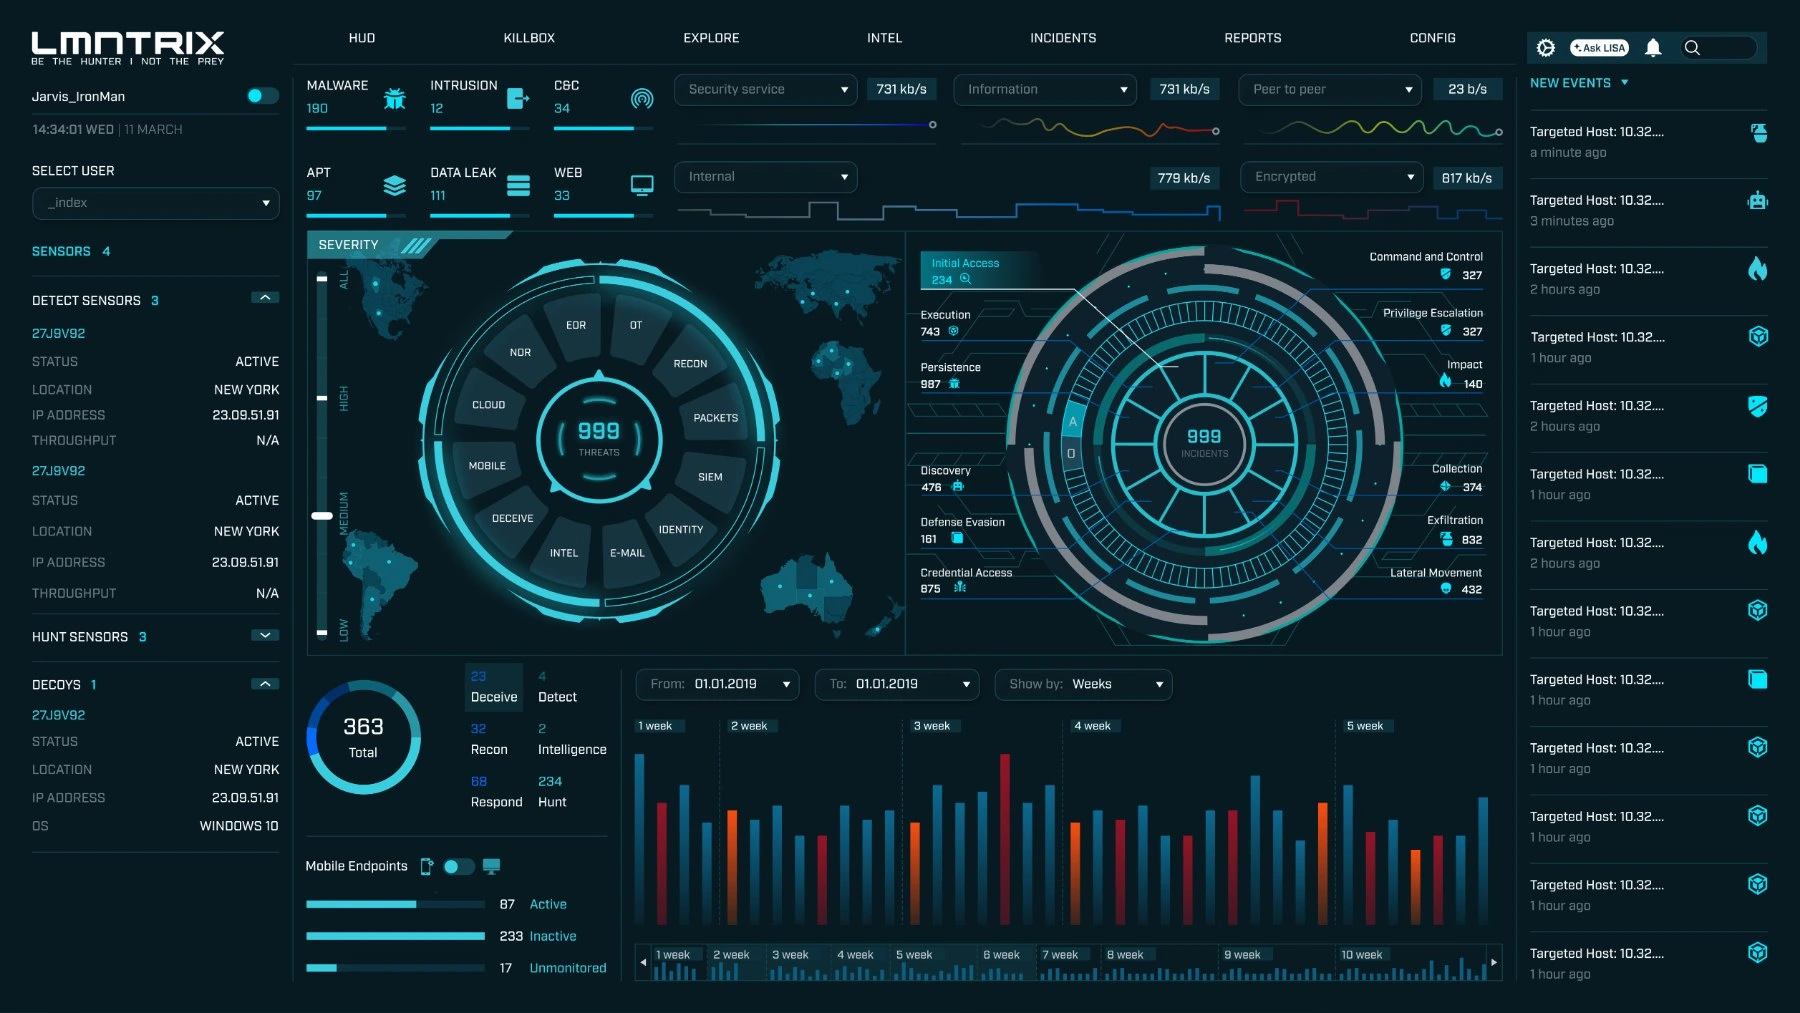
LMNTRIX HUD dashboard showing global threat map and sensor overview
LMNTRIX analytics dashboard with event charts and audit counts
LMNTRIX threat intelligence globe view with indicator search

Comprehensive Threat Prevention, Detection and Response

01

LMNTRIX XDR

Block endpoint, network, cloud and mobile attacks with a proven, lightweight next-gen agent, network sensors and APIs.

  • NGAV, EDR, Mobile Threat Defense, Identity
  • NDR + Network Forensics + SIEM
  • Cloud Security (CSPM, CDR, EP)
  • Machine & Underground Intelligence
02

Full Visibility & ML-Driven Detection

Find stealthy threats with the solution that achieved the best combined MITRE ATT&CK detection & protection scores.

  • Machine Learning and Analytics
  • Correlation, IOC & BIOC Rules
  • Rogue Device Discovery & Asset Management
  • Vulnerability Assessment
03

Accelerated Investigations

Quickly analyze attacks by grouping alerts into incidents and viewing rich investigate context.

  • Incident Management
  • Root Cause Analysis & Cross-Data Insights
  • Live Terminal for Direct Endpoint Access
04

Advanced Threat Hunting

Uncover hidden threats with a powerful Query DSL querying language.

  • XQL Query Language
  • Integrated Threat Intelligence
  • Active Threat Hunting
05

Coordinated Response

Swiftly contain fast moving threats across key enforcement points.

  • Search and Destroy
  • Script Execution
  • File Block, Quarantine, Removal, Device Isolation
  • Automatic Containment Across Network & Cloud
UNDER THE HOOD

14 modules. One platform.

Fortify. Automate. Supercharge. Extend protection from the endpoint to the cloud with complete visibility, military-grade protection, and automated response. Discover the power of hyper-converged LMNTRIX XDR.

EDRNDRCloudEmailAI SecurityMobileIoT/OTIntelligenceValidateDeceiveIdentityPacketsSIEMRecon
LEVEL UP WITH

Level Up with
Layers of Expertise

Get the capabilities of a modern SOC overnight without the cost and headache of managing one.

  1. 01EVENT ANALYST · TIER 1Triage every signal, 24/7. Nothing reaches you unvalidated.
  2. 02INCIDENT ANALYST · TIER 2Investigate confirmed detections and build the incident timeline.
  3. 03INCIDENT RESPONDER · TIER 3Contain and remediate on your behalf, surgically, in under 30 minutes.
  4. 04FORENSIC & MALWARE ANALYSTSReverse the payload, recover the evidence, establish root cause.
  5. 05APT HUNTINGRun the Hunt Cycle — Survey, Secure, Detect, Respond — across your environment continuously.
  6. 06INTEL ANALYSTSMap global threat activity to your industry, geography, and attack surface.
  7. 07INTEGRATION, OPERATIONS & MAINTENANCEKeep every sensor tuned, every integration live, every dashboard current.
WHAT'S INCLUDED

Managed
Detection
and Response
(MDR)

Stop attacks 24/7 with continuous monitoring, proactive threat hunting, alert triage, investigation and response built on LMNTRIX XDR.

  • 01

    24/7 Monitoring
    and Response

    Ensures your network is secure anywhere, every minute, of every day.

  • 02

    Surgical
    Remediation

    Surgical containment and remediation performed in under 30 minutes, eliminating the cost and burden of reimaging.

  • 03

    Unlimited DFIR

    Rely on our forensics and IR experts to stop breaches and deliver outcomes.

  • 04

    Proactive
    Threat Hunting

    Leverage our proprietary Hunt Cycle - Survey, Secure, Detect, Respond to shine a light into the darkest corners, leaving adversaries with nowhere to hide.

  • 05

    Reduce TCO with
    Instant ROI

    Fewer Alerts, More Context. Get the capabilities of a modern SOC without the cost and headache of managing one.

  • 06

    5x Faster
    MTTD & MTTR

    30-minute MTTR makes LMNTRIX MDR the fastest MDR service in the business.

THE AI SOC

Agentic AI that investigates. Human experts who decide.

Artemis works every detection like a senior analyst — in seconds, not shifts. Our analysts validate and act.

ARTEMIS

Agentic investigation engine

Correlates across all 14 modules and builds the incident timeline.

  1. Telemetry pulled
  2. Attacker path rebuilt
  3. Blast radius scored
  4. Containment drafted
  5. Analyst approves
LISA

Your ChatOps assistant

Ask about any incident in plain language — from the console, Slack, or Teams.

What happened on this host last Tuesday?

Suspicious PowerShell activity was contained before lateral movement.

THE CUSTOMERS

Why clients love working with LMNTRIX

The smart money is now finding its way to outcome-based services. The enlightened now seek non-log and SIEM-based services that suppress false positives, using advanced detection and response capability to alert only to “validated breaches” with precise and timely remediation and recovery actions.

Eduard Pieters

“Our approach to detection is something we take seriously. While many MDR companies can set up a SOC and connect with various technologies to pass on alerts, LMNTRIX stands out by providing the critical context we need. They bridge the gap between us and our tools, delivering insights that truly matter. It's like LMNTRIX is playing chess, while others are just playing checkers.”

Eduard Pieters Group Chief Technology Officer, Acclime
  • lmntrixMatt Kraus IT Manager, Alliance Funding Group

    “I couldn't believe the level of detail during testing using an unannounced red team. In real time, LMNTRIX analysts were baiting attackers and actively pursuing them in our environment - it was like something out of a movie.”

  • lmntrixKim Green CISO, World Market

    “LMNTRIX XDR didn't just do one thing; it covered all the bases. Endpoint, network, cloud, mobile, identity, moving target defense and proactive threat hunting. To build this ourselves, we'd need 50 different products, and then we'd need to find security analysts capable of managing them all. The hyper-converged and holistic approach that LMNTRIX takes is a real game changer in my opinion.”

  • Victor YeoVictor Yeo Head of Information Security, Dentons Rodyk

    “LMNTRIX seamlessly integrates with our team, making their analysts an extension of our own resources. Their deep understanding of our environment allows my internal team to focus on other essential security initiatives that drive Dentons' success.”

  • Derek ChenDerek Chen Head of IT Security & Governance, Team Global Express

    “LMNTRIX was the only one that substantiated its cloud detection capabilities — the sole provider that developed its own detections rather than relying on the cloud provider's.”

THE INTEGRATIONS

LMNTRIX is compatible with the
cybersecurity tools you already have

We detect far more threat vectors because we cover more tech. LMNTRIX is compatible with a growing list of security telemetry providers such as those above, and many others.

We can provide the technology you need from our award-winning portfolio, or our XDR can leverage your existing cybersecurity technologies to detect and respond to threats. Telemetry is automatically consolidated, correlated, and prioritized with insights from the LMNTRIX tech stack and the LMNTRIX Threat Intelligence.

Compatible with CrowdStrike, Palo Alto Networks, Microsoft, Darktrace, Fortinet, Sophos and Mimecast.

THE PROOF

Don't take our
word for it.
Take 30 days.

We'll deploy LMNTRIX behind your existing controls, at no cost, for 30 days. If we don't surface something your current stack missed, you've lost nothing but the time it took to read this page. If we do, you'll know exactly what you were paying for before — and what you weren't getting.

Prefer a walkthrough first? Book a demoAlready know what you need?

  1. 01

    Operational in your

    environment within hours, not a six-week project.

  2. 02

    Full MDR service

    for the whole 30 days, including hunting, response, and reporting.

  3. 03

    A written findings report

    at the end, whether or not you proceed.

Contact us

Don’t just takeour word for it…

  • Leader
  • Open Source Excellence
  • Top 250 MSSP Companies In The World
  • Users Choice Award

Top rated security

ISO 27001 certified PCI DSS compliant ISO 27001 certified

Talk to our experts

Please fill out the form to get started.